The Arrest of Dutch Hacker Pepijn van der Stap Marks a Chaotic Pivot for the ShinyHunters Cybercrime Syndicate

The recent apprehension of 24-year-old Dutch national Pepijn van der Stap by authorities in the Netherlands has sent shockwaves through the global cybersecurity landscape, triggering a period of unprecedented volatility within the notorious hacker collective known as ShinyHunters. Van der Stap, a convicted cybercriminal previously operating under the handle Umbreon, was taken into custody on or around September 16, 2026. His arrest has acted as a catalyst for a dramatic escalation in aggression by the remaining members of ShinyHunters, who have since pivoted from targeted data theft to high-stakes, brazen extortion campaigns, including the breach of FBI infrastructure and the targeting of the Russian-linked ransomware group Cl0p.
The Double Life of Pepijn van der Stap
The case of Pepijn van der Stap represents a quintessential example of the "Dr. Jekyll and Mr. Hyde" archetype prevalent in modern cybercrime. A resident of Almere and Lelystad, van der Stap managed to maintain a dual existence that baffled even his professional peers. By day, he was a respected software engineer at the Amsterdam-based cybersecurity startup Hadrian and a dedicated volunteer for the Dutch Institute for Vulnerability Disclosure (DIVD). However, under the digital mask of Umbreon, he was a prolific architect of data theft, responsible for a string of breaches that prosecutors estimated netted between €1.5 million and €2.7 million.
Van der Stap’s previous legal entanglements culminated in a 2023 conviction, where he confessed to his role in extorting victims and disseminating stolen data on underground forums like RaidForums and Breached. Sentenced to four years in prison, with one year suspended, he served time before his release in December 2025. Following his release, van der Stap claimed to be on a path toward redemption, securing a position as an offensive security lead at the Dutch firm Neo Security. Yet, his return to the cybersecurity workforce was short-lived, as the recent investigation by Dutch law enforcement indicates a potential return to his illicit activities.

The Odido Breach and Escalating Tensions
The Dutch police had been under mounting pressure to identify a key suspect in a massive breach of Odido, the nation’s largest telecommunications provider. In February 2026, a native Dutch-speaking ShinyHunters operative utilized sophisticated social engineering tactics to deceive an employee into accessing a spoofed login portal. The resulting breach compromised the sensitive data of over 6.2 million Dutch citizens.
The police released an audio recording of the incident in early September 2026, requesting public assistance in identifying the caller. ShinyHunters brazenly responded to the media, confirming the suspect’s affiliation with their group and promising full legal and financial support for their detained member. Their public defiance, characterized by disparaging remarks toward Dutch law enforcement, signaled a shift in strategy. The group’s communication grew increasingly hostile, warning of further large-scale operations in the Netherlands if authorities continued their pursuit.
A New Era of Brazen Attacks: The FBI and Cl0p
Following the detention of van der Stap, the collective’s operations took a dark and highly provocative turn. Within days of the arrest, ShinyHunters claimed responsibility for an incursion into the FBI’s recruitment portal, apply.fbijobs.gov. The breach exposed the Social Security numbers and personal identifiable information (PII) of more than 5,000 FBI personnel, including those working in sensitive units focused on foreign cyber-espionage and domestic threat assessment.
Security analysts have noted that the data stolen included highly personal psychiatric and medical records, a move that signals a departure from traditional financial extortion toward state-level intimidation. Furthermore, the group turned its sights on Cl0p, a formidable Russian ransomware operation, by launching extortion efforts against them. This represents a rare instance of a "hacker-vs-hacker" conflict on such a significant scale, highlighting the internal fractures and power struggles currently plaguing the digital underworld.

The Influence of Rey and the SLSH Merger
The shift in ShinyHunters’ operational tempo is largely attributed to the influence of a teenage cybercriminal operating from Amman, Jordan, known as "Rey." Rey is a central figure in the ScatteredLapsussHunters (SLSH) alliance, a syndicate formed from the remnants of Scattered Spider, LAPSUS$, and ShinyHunters. According to threat intelligence reports, Rey has been locked in a power struggle with van der Stap for control over the ShinyHunters brand.
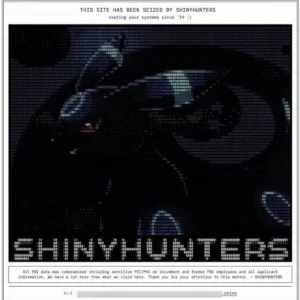
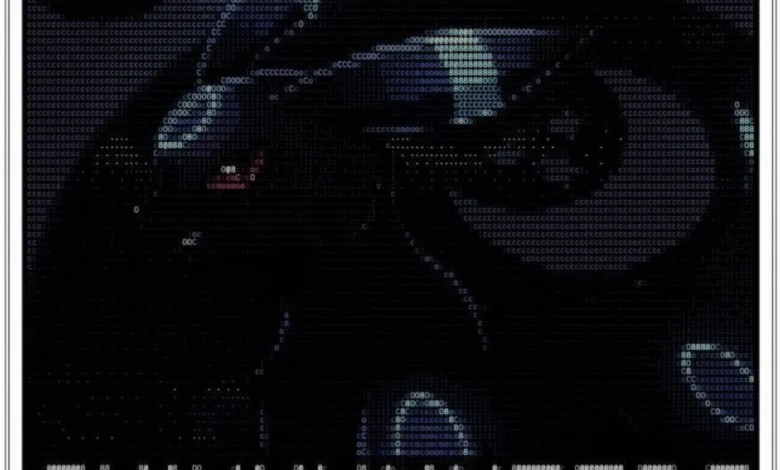
The inclusion of the Umbreon ASCII art—a signature of van der Stap’s previous work—within the defacement files of the FBI jobs site is viewed by experts as a calculated "false flag" operation. By embedding this imagery, Rey and the SLSH leadership likely intended to frame the detained van der Stap for the FBI breach, effectively weaponizing the Dutch hacker’s past against him while simultaneously asserting dominance over the group’s historical brand identity.
Technical Analysis: Exploiting Oracle PeopleSoft
The technical success of these recent attacks is rooted in the mass exploitation of a vulnerability (CVE-2026-35273) within Oracle’s PeopleSoft platform. While Oracle released a patch to address the vulnerability, which ShinyHunters had been using as a zero-day since June, the group demonstrated agility by bypassing web application firewall (WAF) mitigations suggested by Mandiant.
By employing URL-encoding techniques, ShinyHunters successfully neutralized the security measures meant to blunt their exploitation of the PeopleSoft flaw. A joint report by Mandiant and the Google Threat Intelligence Group confirmed that the group used this exploit to compromise a wide array of sectors, including healthcare, agriculture, and government infrastructure. The ease with which the group pivoted between victims underscores the systemic risks posed by the current generation of highly organized, well-funded cybercrime syndicates.

The Broader Impact and Global Implications
The arrest of Pepijn van der Stap and the subsequent actions of ShinyHunters illustrate a critical evolution in the threat landscape. The convergence of professional security researchers with criminal actors, as seen in van der Stap’s career, creates a "knowledge gap" that is increasingly difficult for law enforcement to close. Furthermore, the rise of teenage operatives like Rey highlights the rapid professionalization and global reach of digital insurgencies.
The financial motivation remains high; Mandiant researcher Austin Larsen estimated that ShinyHunters is on track to extract nearly $100 million in extortion payments throughout 2026. This massive influx of capital allows these groups to invest in sophisticated social engineering, hire legal defense, and maintain a state of constant, high-speed evolution that outpaces current defensive frameworks.
As the Rotterdam District Court prepares to hear the case against the 24-year-old suspect on September 29, the focus of global intelligence agencies remains on the shifting alliances within SLSH. The case serves as a stark reminder that the digital battlefield is no longer defined by solitary actors working in the shadows, but by complex, interlinked networks capable of impacting national security and the personal safety of thousands. Whether the arrest of van der Stap will dismantle the core of ShinyHunters or simply accelerate its transformation into a more dangerous, decentralized threat remains a matter of significant concern for cybersecurity policymakers worldwide.
The internal incident at the DIVD—where van der Stap previously volunteered—further complicates the narrative. While the organization reported an incident involving the malicious use of artificial intelligence, it remains unproven if this is linked to the wider ShinyHunters crisis. However, the proximity of these events suggests that the security community is currently undergoing a period of intense scrutiny, as the boundary between the "white hat" research community and the "black hat" criminal element continues to blur with potentially catastrophic consequences for global data privacy and institutional integrity.