Cybersecurity & Protection
-
ZionSiphon Malware Targets Israeli Water Systems, Raising Critical Infrastructure Security Concerns
Cybersecurity researchers have identified a new and sophisticated piece of malware, codenamed ZionSiphon, which exhibits a clear and deliberate focus…
Read More » -
LockBit Dominates Summer Ransomware Landscape Amidst Conti Offshoot Resurgence
Ransomware attacks have surged this summer, with the LockBit group emerging as the most prolific threat actor, relentlessly targeting organizations…
Read More » -
British National Pleads Guilty in U.S. to Leading Scattered Spider Cybercrime Operation, Orchestrating $8 Million Crypto Heist
A British national, identified as a key leader within the notorious Scattered Spider cybercrime collective, has entered a guilty plea…
Read More » -
The Face Behind the Ransomware: Daniil Maksimovich Shchukin Identified as Leader of GandCrab and REvil
The shadowy figure operating under the moniker "UNKN," or "UNKNOWN," who helmed some of the most disruptive ransomware operations in…
Read More » -
Experts Uncover Critical "By Design" Weakness in Model Context Protocol, Threatening AI Supply Chain
Cybersecurity researchers have identified a fundamental architectural flaw within the Model Context Protocol (MCP) that could enable remote code execution…
Read More » -
Massive "0ktapus" Phishing Campaign Exploits Multi-Factor Authentication, Compromising Over 130 Companies and 9,931 Accounts
A sophisticated and sprawling phishing campaign, dubbed "0ktapus" by cybersecurity researchers, has successfully ensnared over 130 companies worldwide, leading to…
Read More » -
Beyond Ransomware: Why Business Continuity, Not Just Backup, is Crucial for Survival
Ransomware and sophisticated cyberattacks frequently capture headlines, painting a vivid picture of data loss and operational paralysis. However, the narrative…
Read More » -
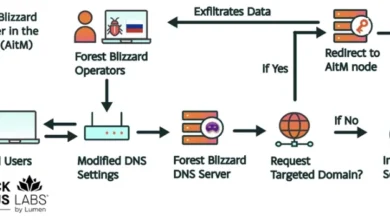
Russian Military Intelligence Exploits Vulnerable Routers for Mass Harvesting of Microsoft Office Authentication Tokens
Hackers associated with Russia’s military intelligence units have been conducting a sophisticated espionage campaign, leveraging well-known vulnerabilities in older Internet…
Read More » -
The AI Demo Illusion: Bridging the Chasm Between Promise and Production Reality
The allure of artificial intelligence has never been more potent, particularly when witnessed in the polished confines of a product…
Read More » -
China-Based APT TA423 Leverages Sophisticated Watering Hole Attacks to Deploy ScanBox Reconnaissance Tool
A China-based advanced persistent threat (APT) group, identified as TA423 and also known as Red Ladon, has intensified its cyber-espionage…
Read More »
