Australian Authorities Dismantle TeamPCP Cybercrime Syndicate in Landmark Supply Chain Prosecution

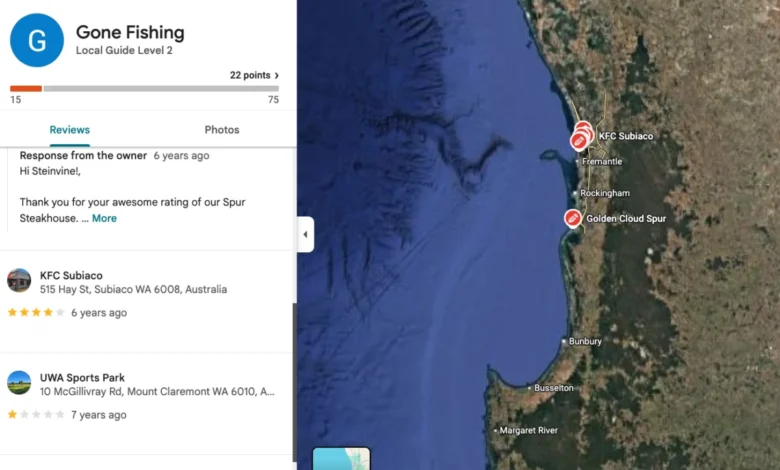
The Australian Federal Police (AFP) have successfully apprehended two men from Western Australia, marking a significant milestone in the global effort to neutralize TeamPCP, a notorious cybercrime syndicate responsible for the most persistent and damaging software supply chain attack spree in recent history. The suspects, identified by local authorities and subsequent reporting as 21-year-old Ruben Ian Thomson and 23-year-old Michael Gaebler, were taken into custody following a coordinated international investigation involving the AFP, the U.S. Federal Bureau of Investigation (FBI), and Western Australian Police. The duo faces a combined total of 14 charges related to the creation and distribution of malicious open-source software, a campaign that reportedly compromised thousands of global businesses and compromised critical cloud infrastructure.

The arrests represent a dramatic conclusion to a year-long reign of terror that saw the group exploit the fundamental trust models underpinning the global software development ecosystem. By weaponizing open-source code, TeamPCP managed to bypass traditional security perimeters, turning the very tools used by developers into conduits for data theft and extortion.
A Chronology of Chaos: The Rise of Shai-Hulud
TeamPCP emerged in late 2025, quickly establishing a reputation for technical audacity and strategic exploitation. Their methodology centered on the deployment of a self-propagating worm dubbed Shai-Hulud. Unlike traditional ransomware that simply locks files, Shai-Hulud was designed to infiltrate the workstations of software developers, identify credentials for public code repositories such as GitHub and NPM, and silently inject malicious payloads into widely used software tools.

The timeline of their operations reflects a rapid escalation in both scale and ambition:
- September 2025: Initial activities are observed on dark web forums like DarkForums, where members, including the individual using the handle "BulkDMT" (later identified as Ruben Thomson), began advertising infrastructure services and illicit data access.
- March 2026: The group executed a high-profile strike against LiteLLM, an AI gateway connecting users to over 100 large language models. Security firm CloudSEK reported this single operation resulted in the harvesting of cloud service keys and sensitive secrets from more than 2,500 organizations, including major technology conglomerates.
- May 2026: TeamPCP demonstrated its reach by compromising at least 3,800 code repositories on GitHub after a developer inadvertently installed a compromised extension. This month also saw the group launch a "recruitment contest," offering Monero (XMR) prizes to participants who could successfully deploy the Shai-Hulud worm to the most popular software libraries, effectively crowdsourcing their criminal operations.
- August 2026: The investigation reached its zenith with the arrest of Thomson and Gaebler in Perth, effectively halting the primary leadership of the syndicate.
Operational Security and the "Cybercats" Collective
The dismantling of TeamPCP has provided a rare glimpse into the internal dynamics of modern cybercriminal organizations. Security experts, including those from Google Threat Intelligence, characterize TeamPCP not as a rigid hierarchy, but as a "center of gravity" for a loose coalition of threat actors who organized their daily operations via a Matrix chat server dubbed "Cybercats."

The group’s downfall was, in large part, a result of their own failure to maintain adequate operational security (OPSEC). Ruben Thomson, who operated under various handles including "EllisD25," "BulkDMT," and "Deadcatx3," frequently blurred the lines between his criminal identity and his real-life persona. Investigations by security researchers and open-source intelligence (OSINT) analysts revealed that Thomson had used his personal email addresses, family-linked IP addresses, and even a company he founded—ironically named "OPSEC Express"—to conduct and manage his illicit activities.
Furthermore, Thomson’s interactions with the security community were marked by brazenness. He registered an account on the HackerOne bug bounty platform under the name "Deadcatx3," a handle already widely recognized by security vendors as a primary TeamPCP alias. This hubris allowed investigators to map his digital footprint back to his residence in the Cottesloe suburb of Perth.

The Human Factor: Addiction and Ideology
The internal communications of the group, which were shared with researchers and monitored by intelligence platforms, reveal a volatile environment fueled by substance abuse and extremist ideologies. Members of the Cybercats chat frequently discussed the use of potent hallucinogens and narcotics, which often led to extended periods of inactivity followed by erratic outbursts.
The involvement of individuals like Michael Gaebler, who allegedly operated under the handle "@pcpcasper," highlights the intersection of cybercrime and political extremism. Evidence gathered from Telegram channels showed that Gaebler was an active participant in the National Socialist Network, a neo-Nazi organization in Australia. This fusion of technical expertise with radicalized worldviews added a layer of volatility to the group’s operations, making them less predictable than traditional profit-motivated ransomware gangs.

Implications for Software Supply Chain Security
The damage wrought by TeamPCP has left an indelible mark on the cybersecurity landscape. Security researcher Charlie Eriksen of Aikido Security noted that the group effectively exploited a "knowledge gap" between theoretical research and operational deployment. By utilizing AI and Large Language Models (LLMs), the syndicate was able to compress the development lifecycle for their exploits, allowing them to scale operations without the discipline traditionally required of state-sponsored actors.
However, the legacy of TeamPCP is paradoxically seen as a catalyst for much-needed systemic change. The group’s successful compromise of GitHub served as a "humiliating wake-up call" for the tech giant. In direct response to the vulnerability exposed by the Shai-Hulud worm, GitHub and other ecosystem maintainers have implemented mandatory "cooldown" periods for automated dependency updates. This mechanism provides a buffer window for security teams to detect and remediate malicious code before it propagates through the software supply chain.

Legal Outcomes and Future Outlook
In the immediate aftermath of the arrests, the legal system has moved swiftly. At the Perth Magistrates Court, it was confirmed that Ruben Thomson was denied bail, reflecting the severity of the charges and the potential risk to public infrastructure. Michael Gaebler’s legal representation did not contest his continued detention, and both remain in custody pending a further court appearance scheduled for September 18.
The broader implications for the cybersecurity sector are profound. The TeamPCP case demonstrates that even highly capable actors can be brought down by a combination of rigorous international law enforcement cooperation and meticulous OSINT work. It also highlights the urgent need for developers and organizations to adopt a "zero-trust" approach to open-source dependencies. As the industry grapples with the fallout, the lessons learned from the "Cybercats" investigation will likely inform future security protocols for years to come.

While the primary actors are now behind bars, the threat posed by the decentralized nature of these cybercrime networks remains. The ability of such groups to recruit and incentivize amateur hackers through competition and monetary reward poses a persistent challenge to global digital stability. For now, the successful prosecution of Thomson and Gaebler serves as a stern warning to those who operate under the false assumption that the internet provides an impenetrable shroud of anonymity. The "center of gravity" for TeamPCP has been neutralized, but the vulnerability of the open-source ecosystem remains a primary concern for global stakeholders in the ongoing battle against sophisticated, agile, and increasingly dangerous cybercriminal threats.
Related posts: