New SEO-Optimized GitHub Malware Campaign Targets Major Software Brands and Deploys Previously Undocumented Rapuncel Infostealer

A sophisticated, large-scale cyberespionage and credential-theft campaign is actively exploiting search engine optimization (SEO) poison tactics via GitHub repositories to impersonate at least 40 prominent software brands, including popular password management solutions. Joint threat intelligence investigations conducted by security researchers at LastPass and Delphos Labs have uncovered that this multi-tiered attack chain relies on a previously undocumented information-stealing malware designated as "Rapuncel."
Compounding the severity of the threat, the campaign leverages a legitimate, Microsoft-signed kernel-level driver that is systematically weaponized to neutralize 145 distinct antivirus and endpoint detection and response (EDR) products. The operation represents a significant escalation in software supply chain impersonation, utilizing manipulated search rankings to lure unsuspecting enterprise and consumer users into downloading deeply malicious software packages disguised as essential utilities, such as authentication applications.
Anatomy of the Attack Chain and SEO Poisoning
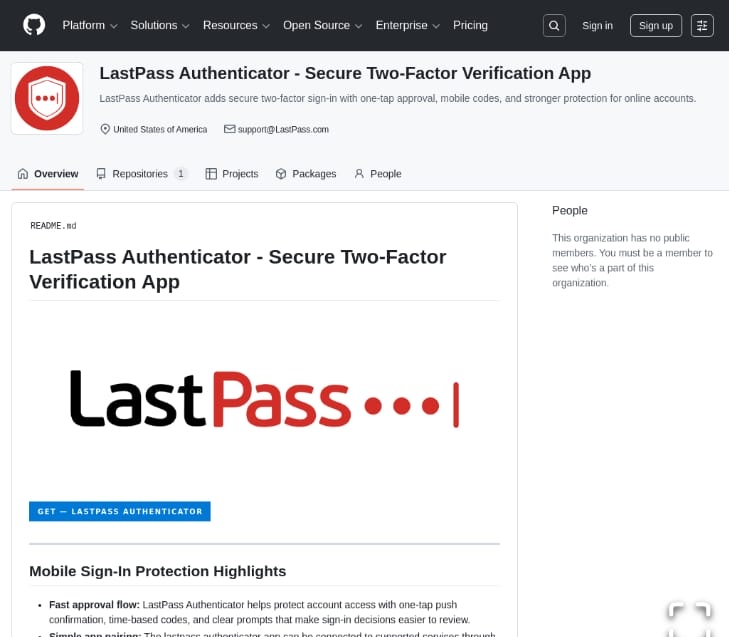
The meticulously engineered intrusion lifecycle begins when targeted victims utilize search engines looking for legitimate utilities, most notably the LastPass Authenticator or other widely adopted productivity and security tools. Threat actors have successfully manipulated search engine algorithms—a technique commonly known as SEO poisoning—to push malicious GitHub repository links to the top of search results.
Upon clicking these deceptive links, users are directed to meticulously crafted GitHub pages that mimic authentic software distribution hubs. When the victim initiates a download by clicking the provided UI buttons, they are routed through an intricate series of HTTP redirections. This redirection maze ultimately leads to independent payload-delivery servers controlled by the malicious operators.
To circumvent automated security scanning systems, network intrusion detection appliances, and browser-based download protections, the servers transmit oversized ZIP archives. These compressed files have their file sizes artificially inflated—sometimes reaching up to 148 megabytes—using padding data specifically designed to bypass inspection thresholds on various security gateways.
Inside the ZIP archive, the primary installer is actually a weaponized copy of ‘vsdbg.exe’, a legitimate Microsoft Visual Studio CoreCLR Debugger component. The threat actors rename and configure this binary to perform DLL sideloading, forcing it to load a malicious companion file named ‘vsdbg.dll’. This sideloading mechanism successfully executes the primary Rapuncel infostealer payload alongside a malicious kernel driver known as ‘Alinubx.sys’, which is tasked with the systematic termination of defensive security software.
Weaponization of Legitimate Infrastructure and EDR Bypass Techniques
One of the most concerning technical elements of the Rapuncel campaign is the attackers’ abuse of legitimate code-signing ecosystems. The Alinubx.sys kernel driver deployed during the infection process is signed through Microsoft’s authentic Windows Hardware Compatibility Publisher certificate chain. Because the driver possesses a valid signature from a trusted authority, the Windows operating system loads it into kernel space without triggering standard driver-signing enforcement warnings. Furthermore, at the time of discovery, the driver had not yet been added to Microsoft’s known vulnerable drivers blocklist.
To blend in with legitimate system operations, the driver is disguised as an NVIDIA component named ‘nvfsflt64.sys’ and registers within the Windows service control manager under the guise of the NvFsFilter service. Once loaded with kernel-level privileges, the driver executes its primary function: acting as an advanced EDR killer. It cross-references a hardcoded internal list containing 145 enterprise-grade antivirus and endpoint detection and response processes, targeting them for immediate annihilation.
LastPass researchers detailed the precise mechanism used by the driver to subvert core operating system protections. "The driver calls ObOpenObjectByPointer with AccessMode=KernelMode, which bypasses the normal user-mode SeAccessCheck path at handle-open time," LastPass noted in its technical advisory. "It asks the kernel to open the process as kernel code, then kills it. That is why it can defeat Protected Process Light (PPL); the protection many security products rely on to survive an administrator."
While the primary objective observed in this current campaign is the termination of security agents, forensic analysis of Alinubx.sys revealed that the driver possesses advanced, latent capabilities. These include file and registry hiding mechanisms, unauthorized dynamic-link library (DLL) injection routines, driver and process interception frameworks, network traffic manipulation utilities, and port redirection features—though these additional functions appear to remain dormant or unactivated in the current wave of attacks.
Operational Mechanics of the Rapuncel Infostealer
With endpoint security monitoring neutralized and defensive processes forcibly closed by the kernel driver, the Rapuncel infostealer initiates its data harvesting phase across the compromised workstation. The malware is engineered to sweep the local system for high-value data, including cached credentials, sensitive session tokens, cryptographic wallet data, browser history, autofill information, and configuration files associated with various productivity applications.
A notable technical hurdle faced by modern infostealers is Google’s app-bound encryption protection, a security feature implemented in Chromium-based browsers like Google Chrome and Microsoft Edge to prevent unauthorized extraction of sensitive cookie and password databases. To bypass this cryptographic barrier, Rapuncel utilizes a specialized evasion technique: it injects a dedicated helper DLL directly into the target browser application and subsequently invokes its own custom Elevation Service to read the protected data stores.
Once the information harvesting routine is complete, Rapuncel compresses the stolen data into an archive and transmits it to an external command-and-control endpoint located at the IPv4 address 2.26.126[.]50. The data exfiltration is executed via raw TCP connections utilizing manually formatted HTTP requests, deliberately bypassing standard higher-level API libraries to avoid routine network monitoring signatures.
To maintain long-term unauthorized access, Rapuncel achieves persistence by establishing a dedicated Windows service. This ensures that the malware automatically restarts following system reboots. Additionally, the malware implements a continuous watchdog mechanism: if any terminated security software attempts to restart or recover automatically, the persistent service detects its revival and immediately terminates the security process again before executing its primary payload loops.
Attribution and Technical Roots
Security analysts from LastPass and Delphos Labs have assessed with moderate confidence that Rapuncel shares substantial code overlap, behavioral similarities, and structural lineage with BoryptGrab, a known information-stealing family. Furthermore, forensic artifacts recovered from the loader components indicate that the initial delivery mechanisms and crypters were constructed using Cruciferra PUROSANGUE, a commercial-style packing and obfuscation suite frequently utilized by cybercrime actors to hinder reverse engineering and static signature detection.
The campaign’s breadth—targeting upwards of 40 distinct software brands across diverse technology sectors—underscores an industrialized approach to malware distribution. By casting a wide net through poisoned search results, the operators maximize their return on investment, successfully ensnaring both corporate users seeking developer utilities and casual consumers looking for everyday software tools.
Broader Implications for Software Supply Chains and Enterprise Defense
The discovery of the Rapuncel campaign highlights persistent structural vulnerabilities in the modern software acquisition lifecycle. The abuse of search engine advertising and organic SEO optimization to host malware on trusted code-hosting platforms like GitHub erodes trust in open-source and community-driven repositories. Developers and IT administrators alike frequently rely on quick internet searches to locate libraries, debugging tools, and application installers, making them prime targets for repository-squatting and brand-impersonation attacks.
Furthermore, the weaponization of validly signed Microsoft hardware compatibility drivers points to an ongoing systemic challenge within the Windows driver ecosystem. Despite continuous efforts by Microsoft and the broader cybersecurity community to maintain and update the vulnerable driver blocklist, malicious actors continue to discover, acquire, or abuse signed binaries that grant them kernel-level execution privileges. This capability effectively neutralizes the isolation models upon which modern Endpoint Detection and Response platforms depend.
Security experts emphasize that traditional perimeter defenses and reactive endpoint monitoring are insufficient against threats that actively blind security software at the kernel level. Organizations are strongly urged to implement strict application control policies, restrict administrative privileges, and deploy behavior-based monitoring that can detect anomalous driver loading events prior to process termination.
Recommended Mitigations and End-User Guidance
In light of the ongoing threat posed by the Rapuncel campaign, cybersecurity authorities and incident responders have issued several core recommendations for both enterprise networks and individual users:
- Direct Software Acquisition: Users should exclusively download software, patches, and updates directly from official vendor domains. Navigating to software repositories via search engine results or sponsored links should be avoided whenever possible.
- Search Result Caution: Enterprise environments should consider blocking or heavily scrutinizing promoted search engine results, which are frequently leveraged by threat actors to push malicious clone sites and fake repositories.
- Repository Verification: Developers and IT professionals utilizing platforms like GitHub should rigorously verify the authenticity of repository owners, check commit histories, and review source code before executing any installation scripts or compiled binaries.
- Endpoint Hardening: Security teams must ensure that their EDR solutions are configured to monitor for unauthorized driver loading, unusual service registrations, and attempts to access sensitive kernel objects via APIs such as ObOpenObjectByPointer.
- Monitoring and Response: Organizations should maintain comprehensive network visibility to detect raw TCP exfiltration patterns and anomalous outbound connections directed toward unverified external IP addresses.
As threat actors continue to refine their use of legitimate code-signing infrastructure and SEO manipulation techniques, defending against sophisticated infostealers like Rapuncel will require heightened vigilance, proactive threat hunting, and a Zero Trust approach to software provenance across all operational tiers.